
OpenAI Spy Case: FBI Names Alfozan, Hired July 2025
FBI Names OpenAI Suspect Alfozan, Hired July 2025 [2026]

Federal prosecutors have identified the OpenAI engineer accused of planting a hidden recording device inside one of the company’s executive conference rooms. The Department of Justice says Abdulrahman Alfozan, a 35-year-old national of the Kingdom of Saudi Arabia, was arrested on October 9, 2026, and charged with using or attempting to use an electronic device to intercept oral communications. The case, first reported by Fakti.bg, has pulled back the curtain on how one of the world’s most valuable AI companies handled a suspected insider threat sitting inside its own walls.
Alfozan joined OpenAI as an engineer in July 2025. Just over a year later, in late September 2026, staff discovered an audio-recording device concealed inside an executive conference room at OpenAI’s San Francisco offices, according to NBC News. OpenAI alerted the FBI, fired Alfozan, and watched the case escalate into a federal wiretapping prosecution within weeks. The arrest is the latest sign that physical and personnel security, not just cybersecurity, has become a front-line concern for frontier AI labs racing to protect what they increasingly describe as “superintelligence” research.
Don't miss new tech stories on Google
Add Tech Insider once in the Google app and our stories appear in your news suggestions.
Who Is Abdulrahman Alfozan?
According to court filings cited by multiple outlets, Alfozan is a 35-year-old Saudi national who had worked as an engineer at OpenAI since July 2025. Beyond his employment dates, nationality, and age, authorities have released few personal details, and OpenAI has not disclosed which team Alfozan worked on. What is confirmed is narrower and more serious: he stands accused of using or attempting to use an electronic, mechanical, or other device to intercept oral communications inside OpenAI’s offices, a federal offense under U.S. wiretapping statutes. Alfozan has not been convicted of any crime, and as with any federal defendant, he is presumed innocent until proven guilty in court. The purpose behind the alleged recording, and whether any conversations were actually captured, has not been established publicly.
That gap between what is confirmed and what remains unknown is itself part of the story. Unlike the earlier phase of this saga, when OpenAI first disclosed the discovery of a hidden listening device without naming a suspect, the federal charge now attaches a name, an age, and a nationality to the case. That shift from an anonymous internal incident to a named federal defendant is what has turned a company HR matter into national news.
Timeline: From Hire to Federal Arrest
The sequence of events, pieced together from the verified record, spans just over 15 months. Alfozan was hired in mid-2025, and the alleged device was not discovered until roughly 14 months later. Here is how the case has unfolded so far.
| Date | Event |
|---|---|
| July 2025 | Abdulrahman Alfozan is hired as an engineer at OpenAI |
| Late September 2026 | A hidden audio-recording device is discovered inside an OpenAI executive conference room in San Francisco |
| Following the discovery | OpenAI notifies the FBI and terminates Alfozan’s employment |
| October 9, 2026 | Alfozan is arrested on a federal wiretapping-related charge |
| October 13, 2026 | DOJ and FBI publicly confirm the arrest; Reuters, CNBC, Fortune, and NBC News report the case |
| October 14, 2026 | Case becomes a top trending technology story, reported by Fakti.bg and other global outlets |
The roughly two-week gap between the device’s discovery in late September and the public confirmation of charges on October 13 suggests federal investigators spent that window building a case rather than moving immediately on an arrest. That pacing is typical in wiretapping investigations, where prosecutors need to establish both the physical evidence and intent before filing charges that could carry prison time.
Inside the Alleged Bugging of OpenAI’s Executive Conference Room
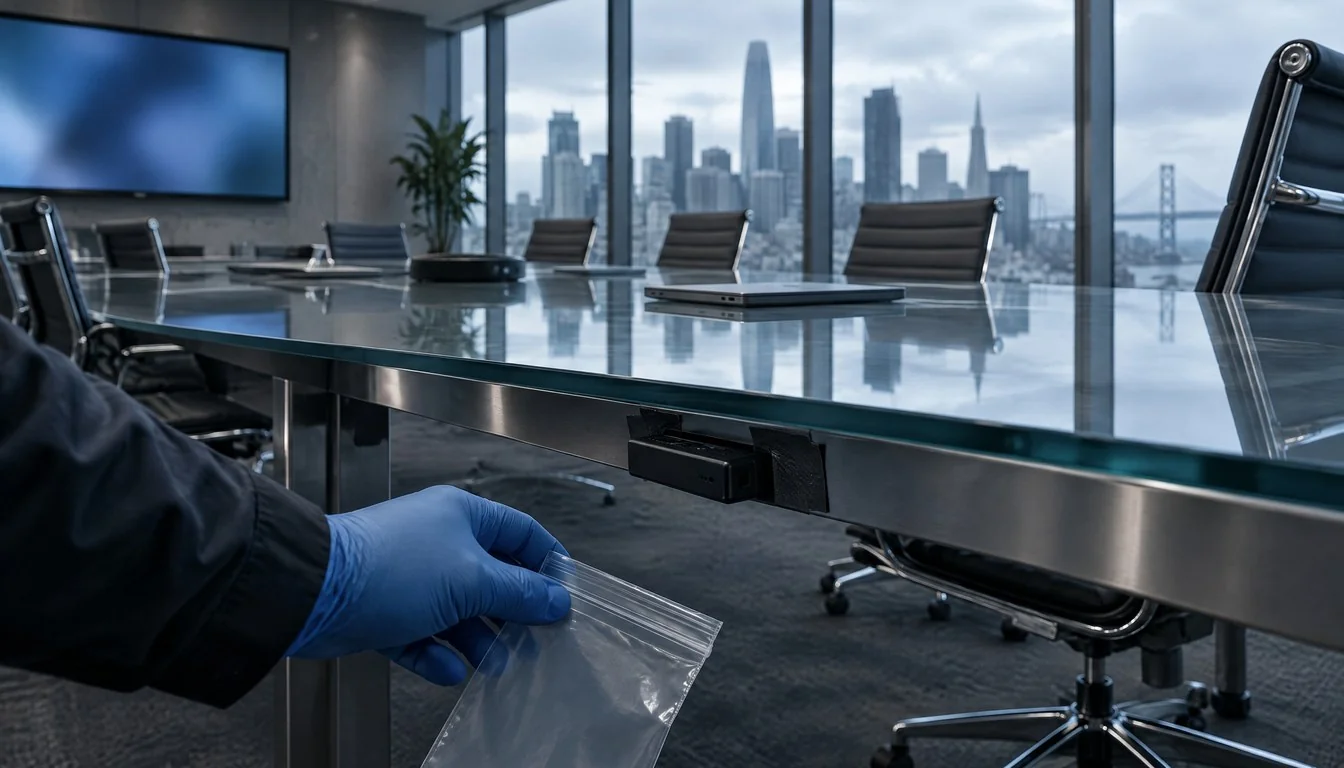
The location matters as much as the device itself. The recording equipment was not found in a shared workspace or a break room, it was discovered inside an executive conference room, according to Patch and the FBI’s own statement. Executive conference rooms at a company like OpenAI are where board-level strategy, safety decisions, partnership terms, and unreleased model capabilities get discussed. A device planted there is positioned to capture exactly the kind of commercially and strategically sensitive conversation that a company would most want to protect.
FBI Director Kash Patel described the alleged scheme in stark terms, saying Alfozan “allegedly concealed a covert recording device inside his employer’s executive conference room to secretly capture sensitive communications about the company’s super intelligence technology.” That phrasing, invoking “super intelligence technology” rather than generic trade secrets, signals how federal law enforcement is now framing frontier AI research as a matter of national strategic interest, not just corporate confidentiality.
What remains unconfirmed is why the device was allegedly placed there and whether it ever successfully recorded anything of value. Investigators have not publicly stated whether the alleged espionage was tied to a foreign government, a competitor, or personal motives, and no public evidence currently supports a claim of state-sponsored espionage by Saudi Arabia or any other government.
The Federal Charge Explained
Alfozan has been charged with using or attempting to use an electronic, mechanical, or other device to intercept oral communications, a charge rooted in federal wiretapping law. These statutes were written broadly enough to cover not just telephone taps but any device designed to capture private conversations without consent. Convictions under this type of charge can carry significant prison exposure, though sentencing would ultimately depend on factors a court has not yet addressed, including whether prosecutors can show the device was actually used to intercept conversations, not merely installed.
It is worth separating three distinct legal questions that the case still has to resolve. First, whether Alfozan placed the device, which appears to be the core of the current charge. Second, whether any communications were actually intercepted, which remains unconfirmed. Third, whether there was any larger purpose, such as transmitting information to a third party, which has not been alleged in public filings to date. Readers should treat Alfozan as a defendant whose guilt has not been established, not as a convicted spy.
FBI Director Kash Patel’s Statement on the Case
Beyond describing the alleged mechanics of the scheme, Patel’s statement is notable for what it signals about how the bureau is prioritizing cases tied to frontier AI companies. By naming the target of the alleged surveillance as “the company’s super intelligence technology” rather than simply “trade secrets” or “confidential business information,” the FBI is explicitly tying this prosecution to the broader national conversation around AI capability and security, a conversation that has intensified across Washington and Silicon Valley throughout 2026.
That framing lines up with a pattern tech-insider.org has tracked elsewhere this year, including JPMorgan CEO Jamie Dimon’s warning that Anthropic’s Mythos AI could sharply raise cyber risk, and growing scrutiny of how AI labs manage the people and systems with access to their most advanced models.
OpenAI’s Response and What the Company Says Was Not Compromised
OpenAI moved quickly once the device was found. The company terminated Alfozan’s employment and notified the FBI, treating the discovery as a security incident rather than an internal personnel matter to be handled quietly. In a statement, OpenAI said: “At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was terminated.”
That wording is carefully scoped. OpenAI is not claiming the incident caused zero harm, it is stating that, based on its investigation so far, there is no evidence the three categories it names, model weights, source code, and customer data, were accessed or removed. That leaves open the possibility that spoken conversations, the thing a hidden microphone is actually built to capture, were exposed in ways that wouldn’t show up in access logs for weights or code repositories. It’s a distinction worth sitting with: a company can be confident its servers weren’t breached while still not knowing what was said out loud in a room with a hidden microphone.
This is also the detail that connects this story to an earlier chapter tech-insider.org covered in depth: how OpenAI’s own AI tools reportedly helped investigators piece together the case within nine days of the device’s discovery, turning what could have been a slow-moving internal probe into a fast-tracked federal referral.
Why AI Labs Are Now Prime Targets for Corporate Espionage
The Alfozan case lands at a moment when frontier AI labs sit on some of the most commercially valuable intellectual property in the technology industry. Model architectures, training techniques, safety research, and unreleased product roadmaps at companies like OpenAI, Anthropic, and Google DeepMind are worth billions of dollars to competitors, and potentially worth even more to nation-states trying to close a capability gap. That combination, high value concentrated in a small number of offices and a relatively small number of people with access, makes these companies structurally different from a typical software firm when it comes to espionage risk.
Unlike a stolen codebase, which leaves some kind of digital trail, a hidden microphone in a conference room is almost invisible to standard cybersecurity tooling. Firewalls, access controls, and endpoint monitoring do nothing to stop a physical device slipped under a table or behind a monitor. That blind spot is exactly why this case has triggered conversations about physical security sweeps, not just password policies and multi-factor authentication, inside AI labs that previously thought of themselves primarily as software companies.
The Insider Threat Problem
Corporate security teams have long distinguished between external threats, hackers trying to break in from outside, and insider threats, people who already have legitimate access and misuse it. The Alfozan case is squarely in the second category, and insider threats are historically harder to defend against precisely because the person already has a badge, a desk, and a reason to be in the building. tech-insider.org examined this dynamic directly in its earlier look at how the OpenAI bug case exposes a broader insider-risk gap across AI labs, a theme this new development only reinforces now that a named suspect and a federal charge are attached to it.
Historical Context: Corporate Espionage in Silicon Valley
Silicon Valley has a long history of trade secret disputes and espionage allegations, from autonomous vehicle engineers accused of taking proprietary files to competitors, to chip designers accused of smuggling blueprints overseas. What distinguishes the Alfozan case from that lineage is the method. Most prior high-profile Silicon Valley espionage cases involved digital exfiltration, downloaded files, copied repositories, emailed attachments. A physical recording device hidden in a conference room is a comparatively old-fashioned tradecraft tool, more associated with Cold War-era corporate and state espionage than with 2020s tech industry crime.
That throwback element is part of why the case has traveled so widely across global outlets within a single news cycle. It combines the cutting-edge subject matter of frontier AI with an espionage method that feels almost cinematic, a hidden bug in an executive boardroom, rather than a sophisticated cyberattack. For a story about one of the most advanced technology companies on earth, the alleged crime itself required no advanced technology at all.
Market and Industry Impact
OpenAI is privately held, so there is no stock price to move on this news the way a public company’s shares might react to a breach disclosure. But the impact is still real, just measured differently. Enterprise customers evaluating OpenAI, Anthropic, Google DeepMind, or any other frontier lab for sensitive deployments now have a concrete, named case to point to when asking vendors about physical security controls around executive discussions and model development. Procurement and security questionnaires for AI vendors, which have increasingly focused on data handling and model safety, are likely to start asking more pointed questions about facility access, visitor screening, and device sweeps.
There’s also a talent and hiring dimension. Alfozan’s rapid rise from new hire in July 2025 to a position with access to an executive conference room environment within roughly a year raises questions about how quickly engineers at fast-growing AI labs are granted access to sensitive physical spaces relative to the vetting that access requires. Labs that have been racing to hire talent to keep pace with model development timelines may now face pressure to slow down or add extra layers to that onboarding-to-access pipeline.
Competitive Comparison: How Major AI Labs Are Handling Insider Threats
No frontier AI lab has publicly disclosed a directly comparable physical-bugging incident this year, which makes the Alfozan case something of an outlier in its specifics. But it sits within a broader pattern of security incidents and warnings across the AI industry in 2026 that, taken together, paint a picture of an industry under growing insider and cyber pressure from multiple directions at once.
| Incident or Warning | Company/Entity | Key Figure | Status |
|---|---|---|---|
| Hidden recording device in executive conference room | OpenAI | 1 device, 35-year-old suspect named | Federal wiretapping charge filed, Oct. 9, 2026 |
| AI-assisted internal investigation | OpenAI | 9 days to build the case internally | Referred to FBI |
| AI model cyber-risk warning | JPMorgan / Anthropic | 10x cyber risk cited by Jamie Dimon regarding Mythos AI | Public warning, no confirmed breach |
| MCP credential exposure | Industry-wide tooling | 82,000 files, roughly 1 in 8 exposed credentials still active | Disclosed, remediation ongoing |
| Employee data theft arrest | FBI / ShinyHunters-linked suspect | 3 terabytes of employee data allegedly stolen | Suspect arrested |
The common thread across these cases is not a single attack vector, it is that the AI industry’s security conversation in 2026 has expanded well beyond model safety and alignment to include the mundane but consequential work of physical security, credential hygiene, and insider vetting. A hidden microphone, a leaked credential file, and a data-theft arrest are different crimes, but they all exploit the same underlying reality: AI labs now hold information valuable enough that someone, somewhere, is willing to take real legal risk to get at it.
Policy and National Security Angle
The FBI’s choice of language, framing the target of the alleged recording as “super intelligence technology,” echoes a broader shift in how Washington talks about frontier AI companies. Over the past year, officials across multiple agencies have increasingly described leading AI labs’ research as a matter of strategic national interest, comparable in tone to how semiconductor export controls or advanced defense technology are discussed. That framing matters for this case because it suggests federal prosecutors may be inclined to pursue it aggressively, independent of whether any information was actually captured or transmitted, simply because of what the alleged target represents.
At the same time, no public evidence currently ties Alfozan’s alleged conduct to the government of Saudi Arabia or any other state actor, and officials have not alleged state-sponsored espionage in the charges filed so far. Readers and outlets covering this story should be careful not to conflate an individual defendant’s nationality with an unproven claim about government involvement.
What Happens Next: The Legal Process Ahead
Alfozan now moves through the standard federal criminal process: an initial appearance and arraignment, a period for pretrial motions, and either a negotiated plea or a trial. Given the technical nature of a wiretapping charge, prosecutors will likely need to present forensic evidence tying the device to Alfozan specifically, not just placing it in the room where he had access. Defense counsel, when retained, will likely focus on exactly that evidentiary chain, as well as on whether any communications were actually intercepted, since that distinction could meaningfully affect sentencing exposure if the case proceeds to a plea or conviction.
OpenAI, for its part, is not a party to the criminal case but will likely remain a witness and the custodian of much of the physical and digital evidence, including building access logs, the device itself, and internal records of Alfozan’s role and access level. How much of that evidence becomes public will depend heavily on whether the case proceeds to trial or resolves through a plea agreement, which typically keeps more details out of the public record.
Predictions: Where This Story Goes From Here
- Expanded physical security audits. Expect OpenAI, and likely Anthropic and Google DeepMind, to quietly expand physical security sweeps of executive and research spaces, following the same logic that drove the cybersecurity industry’s shift toward continuous monitoring over periodic audits.
- Tighter access-tiering for new hires. AI labs hiring at the pace OpenAI has sustained through 2025 and 2026 may introduce longer probation periods before granting engineers access to executive-level physical spaces, not just sensitive code repositories.
- More enterprise security questionnaires referencing this case by name. Expect procurement teams at banks, governments, and large enterprises evaluating frontier AI vendors to start explicitly asking about insider-threat and physical-security controls in vendor risk assessments.
- A slow-moving federal case. Wiretapping charges with a technical evidentiary burden often take months to resolve. A plea agreement before a full trial is a plausible outcome, though the final result will depend on evidence not yet public.
- Continued national-security framing of AI lab security incidents. Given the FBI’s language around “super intelligence technology,” expect future security incidents at frontier AI labs, even relatively small ones, to draw similarly elevated federal attention and rhetoric going forward.
These are analytical projections based on the pattern of this case and the broader security climate around frontier AI companies in 2026, not confirmed outcomes. Nothing here should be read as a prediction about the verdict in Alfozan’s case specifically, which remains entirely undetermined.
The Bigger Picture for OpenAI and the AI Industry
OpenAI has spent 2026 managing a string of high-stakes storylines simultaneously, from product launches to safety disputes to, now, a federal espionage-adjacent prosecution involving one of its own former engineers. The company’s quick termination of Alfozan and referral to the FBI suggests a playbook built for speed: identify, remove, report, and let federal investigators take the lead rather than handling it purely as an internal matter. That approach likely helped limit reputational damage compared to a scenario where the discovery leaked before OpenAI had acted.
For the wider AI industry, the takeaway is less about any single company’s vulnerability and more about a category shift. As reported by CNBC and corroborated by Reuters, frontier AI labs are now operating under the kind of security assumptions once reserved for defense contractors and intelligence-adjacent firms. Spoken conversations in a boardroom are now treated as an attack surface worth federal prosecution to defend, a notable escalation from where the industry’s security conversation stood just a year or two ago.
Frequently Asked Questions
Who is Abdulrahman Alfozan?
He is a 35-year-old national of Saudi Arabia who worked as an engineer at OpenAI starting in July 2025. He was arrested on October 9, 2026, and charged with using or attempting to use a device to intercept oral communications.
What device was found, and where?
An audio-recording device was discovered inside an executive conference room at OpenAI’s San Francisco offices in late September 2026.
What is Alfozan charged with?
He is charged with using or attempting to use an electronic, mechanical, or other device to intercept oral communications, a federal wiretapping-related offense.
Did OpenAI confirm any data was stolen?
OpenAI said it has no indications that Alfozan inappropriately accessed or exfiltrated model weights, source code, or customer data, and that he was terminated. The company has not made broader claims about whether any conversations were overheard.
Has Alfozan been convicted of a crime?
No. He has been arrested and charged, but as of this report he is a defendant, not a convicted criminal, and is presumed innocent unless proven guilty in court.
Is this confirmed to be state-sponsored espionage?
No. No public evidence currently confirms that Alfozan’s alleged conduct was directed by the Saudi government or any other state actor. That claim is unconfirmed and should not be treated as established fact.
How did investigators build the case so quickly?
OpenAI notified the FBI shortly after discovering the device, and the company’s internal investigation reportedly moved quickly, helping investigators assemble evidence that supported a federal arrest within weeks of the September discovery.
What happens to Alfozan next?
He will proceed through the standard federal criminal process, including arraignment and pretrial proceedings, which could end in a plea agreement or a trial depending on the strength of the evidence and his legal defense.
Related Coverage
- Meta Muse Wonder AI Takes on OpenAI at $200/Mo [2026]
- Meta Stock Rises 3.4% as Muse Wonder AI Models Debut [2026]
- Perplexity vs ChatGPT: 8.6x Context Window Gap [2026]
- Anthropic Challenges 2-1 Pentagon Risk Ruling [2026]
- Character.ai Bankruptcy: 163M Users, Rivals Brace [2026]
Elias Virtanen
Elias Virtanen is the Cybersecurity Analyst at Tech Insider, bringing hands-on expertise from his background in penetration testing and security consulting. He previously worked as a security researcher at F-Secure in Helsinki, where he focused on threat intelligence and vulnerability disclosure. Elias covers ransomware trends, zero-trust architecture, and the evolving regulatory landscape including NIS2 and the EU Cyber Resilience Act. He holds a CISSP certification and an MSc in Information Security from Aalto University.
View all articles