
OpenAI Engineer Arrested for Allegedly Installing Secret Recording Device to Spy on Executive Meetings
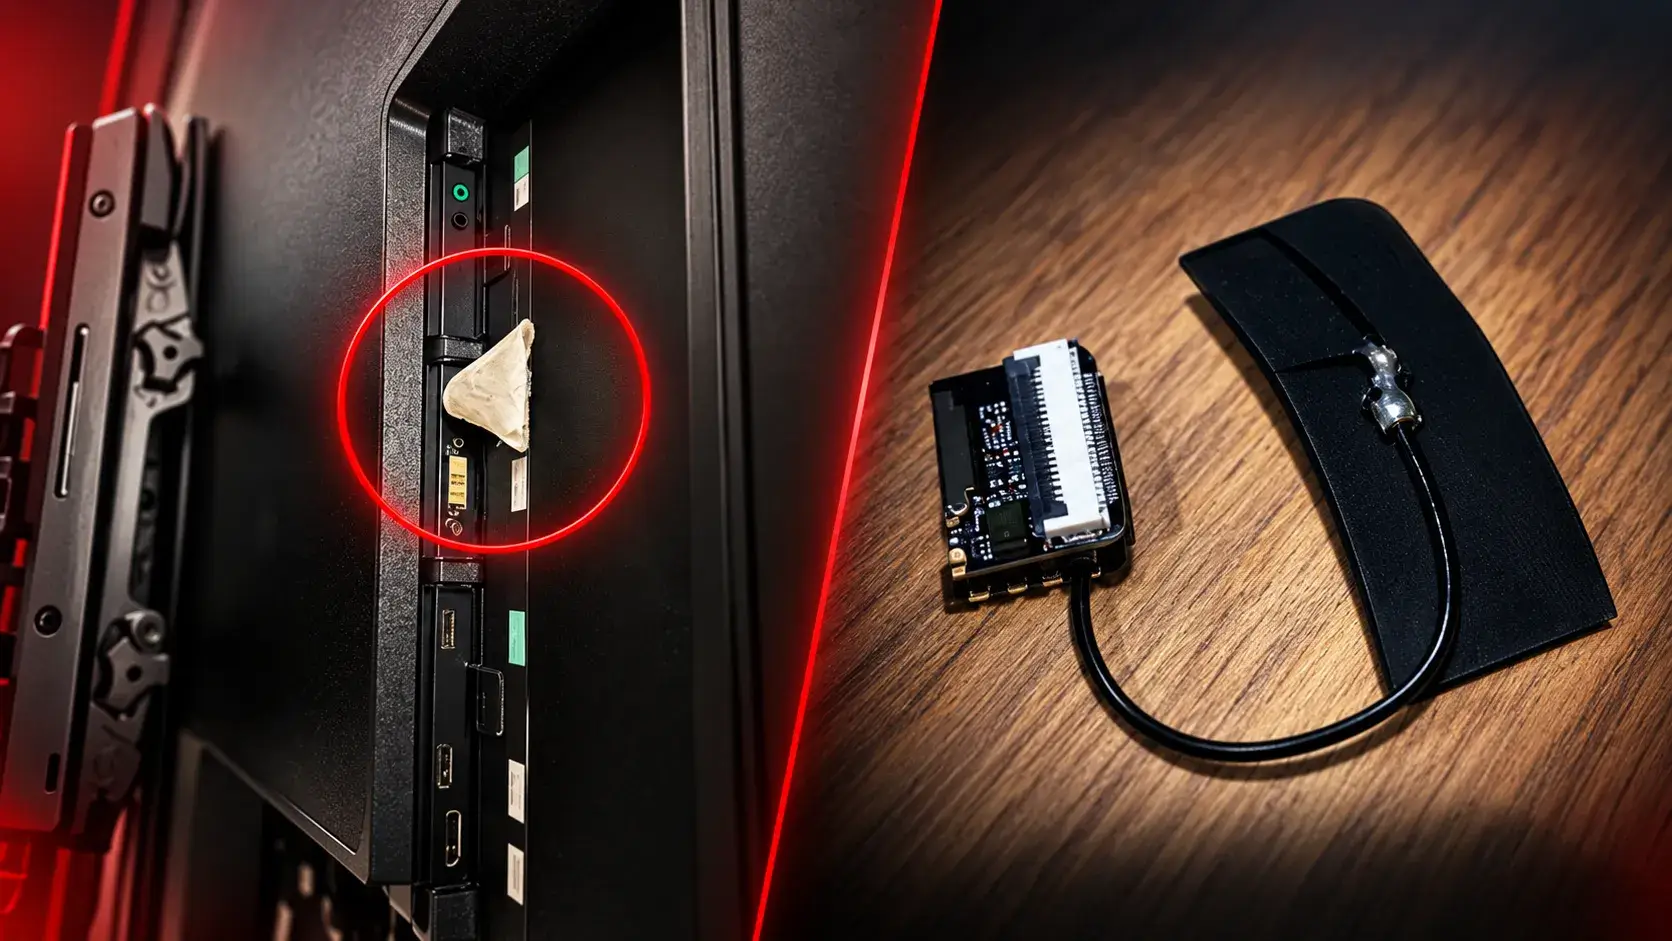

An OpenAI engineer has been arrested for allegedly concealing an audio recording device in an executive conference room at the company’s San Francisco offices.
According to a Justice Department announcement, Abdulrahman Alfozan, 35, a Saudi national, was taken into custody on October 9 and appeared in federal court on October 13, 2026.
OpenAI Engineer Arrested
Alfozan, who has worked at OpenAI since July 2025, faces a charge of using or attempting to use a device to intercept oral communications.
Prosecutors allege that the targeted conference room hosted sensitive discussions regarding proprietary research, product development, commercial relationships, government engagements, and strategic decisions related to the company’s artificial intelligence capabilities.
OpenAI personnel discovered the first recording device on September 30, hidden inside a USB port behind a conference room television. Investigators allege that it was installed around September 28 and disguised with toilet paper. Although OpenAI determined that the contents were encrypted, the announcement does not disclose what investigators ultimately recovered.
The hidden device raises concerns about insider threats: a recording device placed in a sensitive meeting space could capture conversations without compromising corporate applications.
However, the announcement does not clarify whether the device successfully recorded meetings, transmitted audio, or exposed confidential information. Its hardware specifications and operating configuration have not been revealed.
According to the complaint, office surveillance footage shows Alfozan near the executive conference room on multiple times before investigators discovered the device.
He allegedly lacked authorization to access the room or participate in its meetings. Prosecutors further claim that he used a productivity tool to investigate building addresses, room capacities, calendars, and leadership locations.
Investigators also identified relevant prompts submitted through a chatbot account associated with Alfozan’s spouse. The complaint states that this account shared multiple identifiers and characteristics with his account.
Between September 24 and September 30, the prompts focused on continuous audio recording, Wi-Fi customization, live listening, device concealment, remote access, and storage encryption.
Additional prompts allegedly referenced the first device’s custom header and unique MAC address on September 27 and 28. Prosecutors say these details link the account’s inquiries to specific hardware. Nevertheless, the announcement does not confirm who submitted each prompt or whether the requested capabilities were applied to either device.
On October 5, surveillance footage reportedly captured Alfozan entering the executive conference room and looking behind the television. That same day, OpenAI security personnel found an unattended bag in another room containing his wallet, identification, and a second recording device similar to the first.
The FBI is investigating the case, and federal prosecutors are handling it. Officials have characterized the allegations as a national security concern involving the protection of American AI innovation. If convicted, Alfozan faces up to five years in prison, a $250,000 fine, and three years of supervised release. The allegations remain unproven in court.
Update defenses against new malware as soon as it appears. Integrate TI Feeds with data from 16K SOCs.
Hot this week
How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities
How to Build and Run a Security Operations Center (SOC Guide) – 2023
Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component
Web Server Penetration Testing Checklist – 2026
ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities
Topics
- Acquisition
- Adobe
- Adware
- AI
- Amazon
- Amazon AWS
- AMD
- Android
- Anti Virus
- Antimalware
- ANY RUN
- Apache
- API
- Apple
- APT
- Artificial Intelligence
- Avast
- AWS
- Azure
- Backdoor
- Bitcoin
- Bluetooth
- Botnet
- Browser
- Buffer over flow
- Bug Bounty
- Business
- Chatbots
- ChatGPT
- Checklist
- Chrome
- Cisco
- CISO
- CISO Advisory
- Cloud
- Cloud Security
- Cloudflare
- Computer Security
- Course
- CPU
- Cross site Scripting
- cryptocurrency
- Cryptocurrency hack
- CVE/vulnerability
- Cyber Advisory
- Cyber AI
- Cyber Attack
- Cyber Crime
- cyber security
- Cyber security Course
- Cyber Security News
- Cyber Security Resources
- Cybersecurity Newsletter
- Dark Web
- Data Breach
- Data Governance
- DDOS
- Deals
- DeepSeek
- Discord
- DNS
- Dos Attack
- Drive
- Dropbox
- Education
- Email Security
- Ethical Hacking
- Exploit
- Exploitation Tools
- Extratorrents
- Featured
- Firefox
- Firefox News
- Firewall
- Forensics Tools
- game
- GenAI
- GitHub
- GitLab
- Gmail
- Google dorks
- Governance
- GRC
- Hacking Books
- Hacks
- Hardware Hacking
- HBO
- HTML
- HTTP
- IBM
- IIS
- Incident Response
- Information Gathering
- Information Security Risks
- Infosec- Resources
- Insider Threats