
Stylian conducts emergency free check of PHP2Shell vulnerability
 Enlarge image
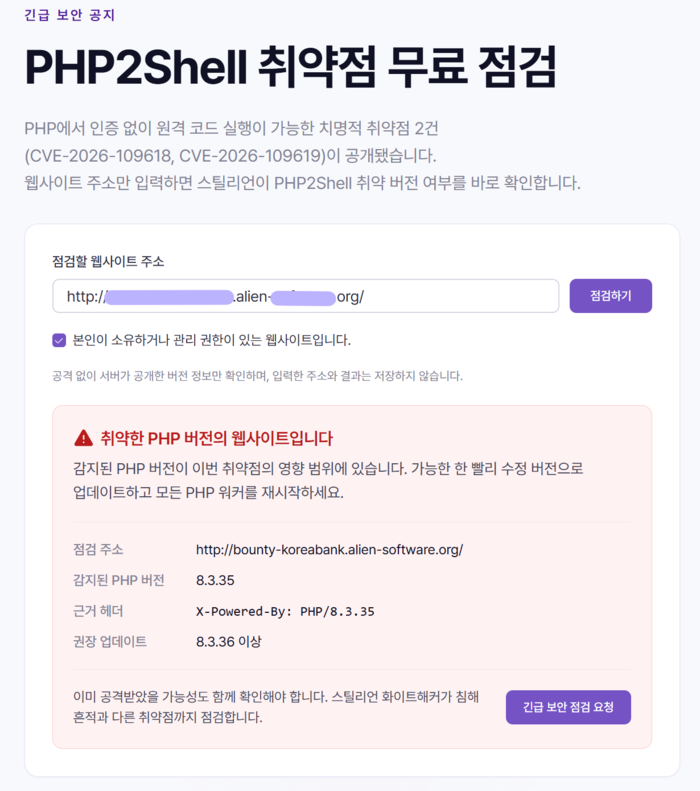
Stealien, an artificial intelligence (AI) security company led by CEO Park Chan-am, announced on the 22nd that it had launched a free online service to check whether a website is affected by the PHP2Shell security vulnerability. Users only need to enter the website's address (URL).
Users can visit the dedicated page on Stealien's website (stealien.com/php2shell) and enter the address of the website they want to check. The service helps security staff and website operators at companies and institutions find risks in their running services and review what steps they need to take next.
The Ministry of Science and ICT and the Korea Internet & Security Agency (KISA) have urged South Korean companies and institutions to update their systems immediately to address the PHP security vulnerability. At noon that day, the Ministry of Science and ICT raised the private-sector cyber crisis warning level from "attention" to "caution" to prepare for the risk of large-scale hacking.
PHP2Shell is a name for two serious security vulnerabilities in PHP, a technology widely used to run web services. The vulnerabilities are CVE-2026-109618 and CVE-2026-109619. Attackers do not need to log in to exploit them. If they succeed, they can run their own code on a server or access sensitive information.
PHP is used by many types of websites and online services, including homepages, online stores, message boards, and administration pages. Website-building tools widely used in South Korea, such as WordPress and Gnuboard, also rely on PHP. These vulnerabilities are problems in PHP itself, not in the code of any one website. This means a website can still be affected if it uses a vulnerable version or setup of PHP, even if the website was built securely.