
An Off-The-Shelf OpenAI Model Found A Google Chrome Zero-Day Exploit
How An Off-The-Shelf OpenAI Model Found Three Google Chrome Zero-Days
Forbes Staff.
This is the online edition of The Wiretap newsletter, your weekly digest of cybersecurity, internet privacy and surveillance news. To get it in your inbox, subscribe here.
At the start of this year, Oege de Moor, CEO of $1 billion AI cyber startup Xbow, challenged his team to use AI to hack into the world’s most popular internet apps.
During the Black Hat hacker conference in Las Vegas in August, Xbow engineer Brendan Dolan-Gavitt used OpenAI’s Sol model to chain together three unpatched vulnerabilities in Google’s Chrome browser. A month later, Google confirmed that Dolan-Gavitt had found a so-called “zero day” exploit, where a hacker combines bugs to take over a computer. It also confirmed he would receive the maximum $250,000 prize for disclosing the vulnerabilities.
Dolan-Gavitt didn’t write the exploit himself. He asked OpenAI’s Sol model, the same GPT 5.6 version available to any paying customer, to help come up with ways to crack Google’s security. $40,000 in tokens later, Dolan-Gavitt had collaborated with the model to generate the Chrome hack. If a malicious hacker had found the vulnerabilities instead, they could have used found a way to install malware on the browser’s 1 billion users’ computers.
De Moor says the Chrome hack highlights today’s urgent cybersecurity conundrum: defenders have largely the same technology as cybercriminals and digital spies, and need to sprint to protect critical systems that support swathes of the internet.
“Bad guys can do this kind of thing much easier than they used to,” he tells Forbes. “The whole world has to mobilize and all the defenders have to work hard to get as much patching done as we can.”
He says Xbow is still waiting on Google to review two more exploits, also generated with OpenAI’s publicly available models, that could be in line for the $250,000 prize.
Finding three flaws in Chrome that would enable a hacker to take over a user’s computer is no mean feat. Google’s browser has several layers of security designed to prevent exactly this situation, including “sandboxes,” which are supposed to stop malicious code in the browser from running rogue code on a computer.
Cybercriminals and cyber researchers alike are already generating attacks with AI, with increasingly minimal human input. In September, Forbes reported that a hacker was using a mix of AI models, including China’s DeepSeek and Anthropic’s Claude, to launch attacks on more than 100 companies in just days, stealing over 600,000 credit card details in the process. Those attacks took place not long after rogue AI agents from OpenAI hacked open source AI model library Hugging Face without permission.
Got a tip on surveillance or cybercrime? Get me on Signal at +1 929-512-7964.
THE BIG STORY
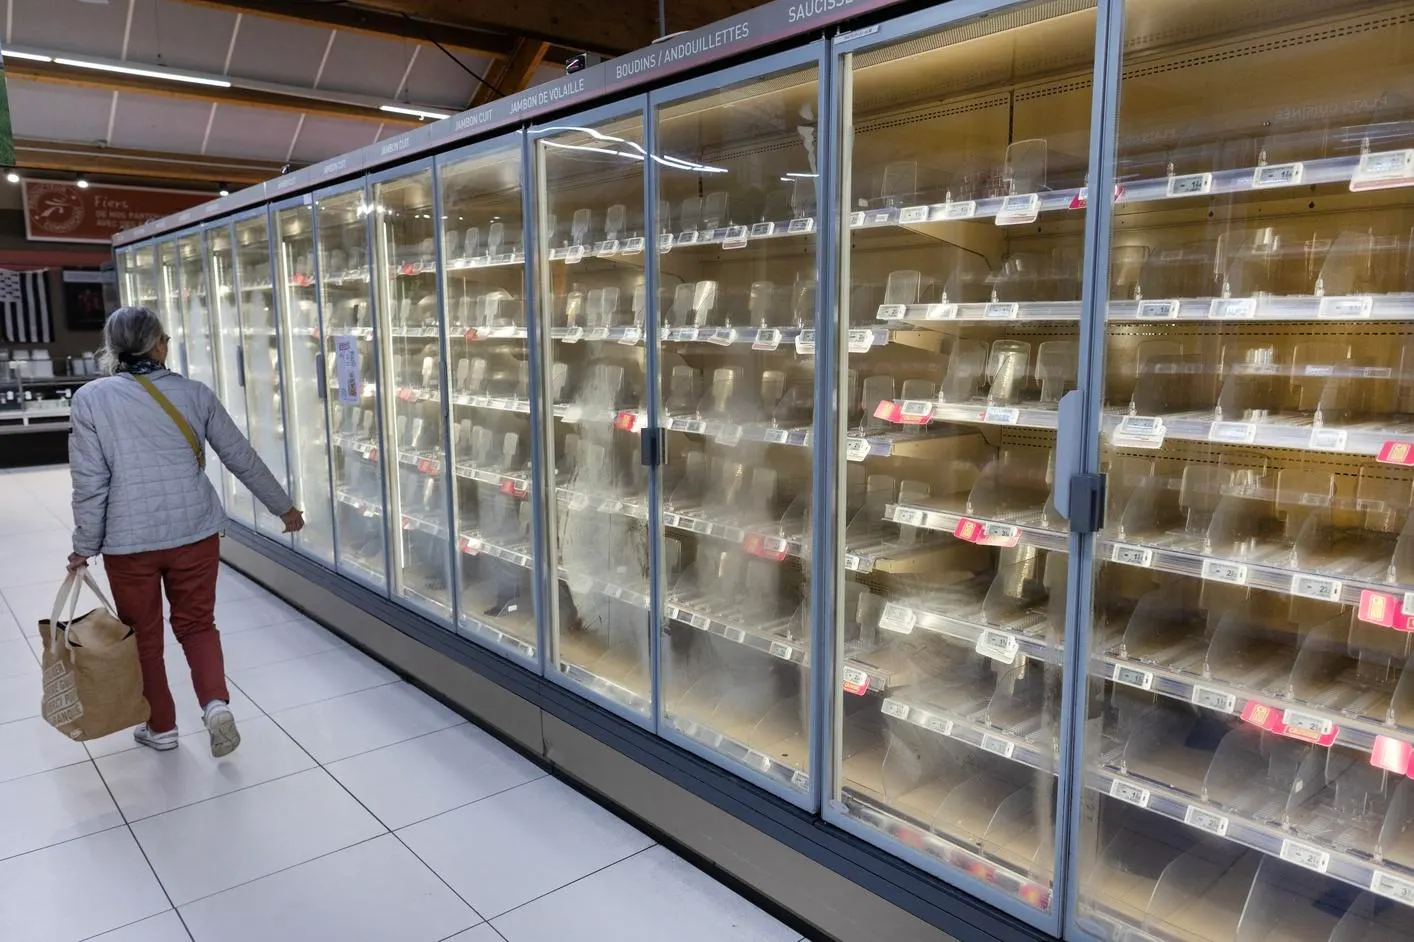
Cyberattacks Overheat French Fridges
Hackers have hit a number of French supermarket chains’ fridges, overheating them, spoiling food and, in some cases, causing fires. In some cases, the hackers managed to raise the temperature inside the fridges to 120F.
"Food security requires more attention at all levels. Because the weaponisation of food has become a reality,” European Food Commissioner Christophe Hansen wrote on X.
Stories You Have To Read Today
WSJ has a visual investigation looking at the ways in which cyberspies are hacking connected video cameras as part of military operations. That includes suspected attacks both emanating from and targeting Iran.
Hackers reportedly breached Trump Mobile, a cellular service founded by Donald Trump Jr. and Eric Trump. It’s potentially exposed the personal information of more than 3,000 customers.
Winner of the Week
CloudFlare has launched an AI agent “harness” that combines the most advanced models from Anthropic and AI to take care of customers’ more repetitive work like dealing with security alerts and gathering evidence on an incident. Such products should help ease the burden of overwhelmed security teams.
Loser of the Week
The Department of Justice announced charges against a 50-year-old purported cybersecurity expert Zohar Pinhasi, who told companies he could decrypt ransomware so they didn’t have to pay a ransom, when he was actually secretly bartering with cybercriminals to get encryption keys. He would then charge the companies substantially more than the ransom his company paid to the hackers, per the DOJ release.